About the Event
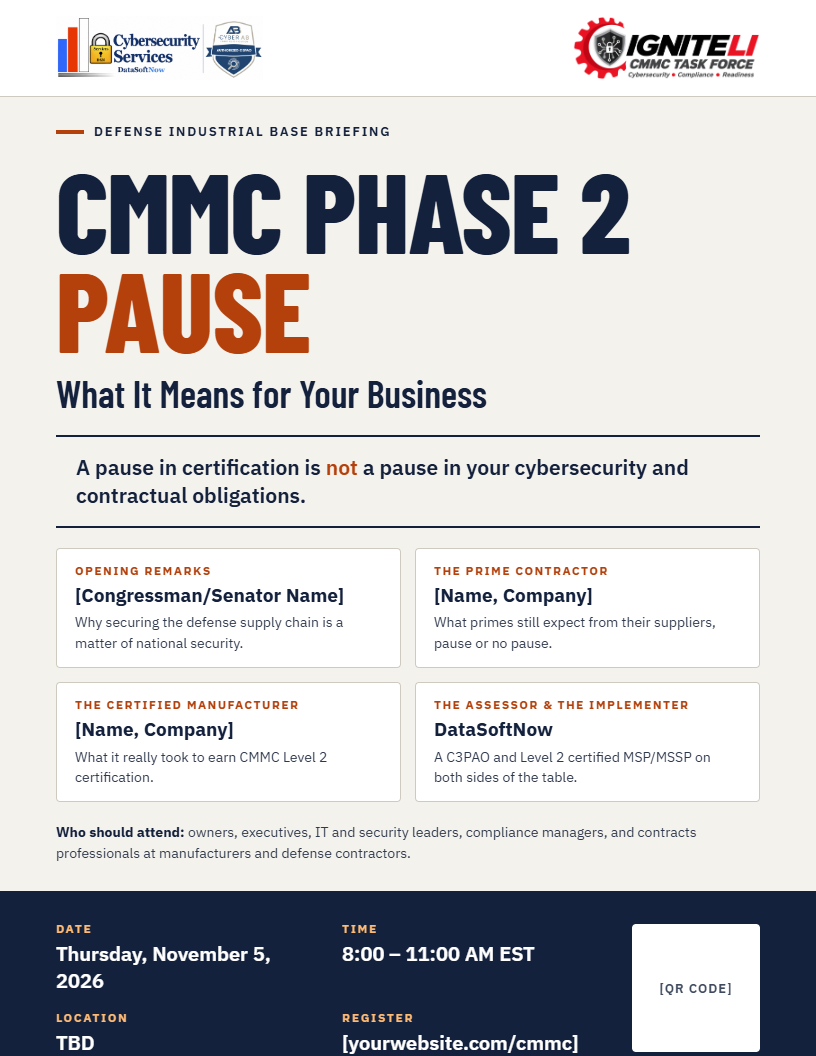
In July 2026, the Department of War paused CMMC Phase 2, the requirement that contractors handling Controlled Unclassified Information (CUI) obtain a third-party C3PAO certification as a condition of contract award. For many local manufacturers and defense contractors, the news raised more questions than answers. Is CMMC going away? Should we stop preparing? What do our primes expect from us now?
The short answer: a pause in the certification timeline is not a pause in your obligations. Phase 1 self-assessments remain mandatory, existing certifications retain their full value, and DFARS cybersecurity requirements are unchanged. Companies are still fully responsible for protecting CUI and face real legal and False Claims Act risk if their self-assessments don’t hold up. And the primes you supply are still flowing cybersecurity requirements down through their contracts.
Join us for a candid discussion opening with remarks from [Congressman/Senator Name], followed by a panel featuring perspectives from across the Defense Industrial Base.
Opening Remarks
[Congressman/Senator Name], [Title, District/State]
Why protecting our defense supply chain is a matter of national security. Adversaries target small and mid-sized suppliers because they are often the easiest path to sensitive defense information, and every stolen design, specification, or technical drawing weakens our military advantage and our economy. [He/She] will discuss the cyber threats facing the Defense Industrial Base, the role local manufacturers play in keeping our warfighters safe, and why strong cybersecurity is essential to keeping defense work and jobs in our community.
Panelists
The Prime Contractor: [Name, Title, Company]
How primes are viewing the pause, why their expectations of suppliers haven’t changed, and what they look for when choosing and retaining subcontractors.
The Certified Manufacturer: [Name, Title, Company]
A manufacturer that successfully earned CMMC Level 2 certification walks through what it really took: the time, the cost, the surprises, and the lessons learned, and why certification is proving to be a competitive advantage, pause or no pause.
The Assessor and the Implementer: [Name(s), Title(s)], DataSoftNow
As both a C3PAO and a CMMC Level 2 certified MSP/MSSP, DataSoftNow brings a rare view from both sides of the table: what assessors look for, where companies most often fall short, and how to use this window to build a program that is genuinely provable rather than just claimed.
What You’ll Take Away
You’ll leave with a clear understanding of what the pause does and doesn’t change, how to protect your current and future contracts, and practical next steps for your cybersecurity and compliance program.
Who Should Attend
Owners, executives, IT and security leaders, compliance managers, and contracts professionals at manufacturers and defense contractors of all sizes.